Recorded business evidence
Stock, orders and financial records stay linked to the operations that created them.
StockChief works from recorded business facts and the authority you configure. Review a prepared action and its consequences before giving approval where required.
Stock movements, purchasing, messages and financial actions have their own permissions and approval paths. A connected account grants API access; your business authority determines which supported work may proceed.
Missing facts, conflicts and unresolved outcomes stay available for review. Ask can explain the records behind a result.
Explore the actual product →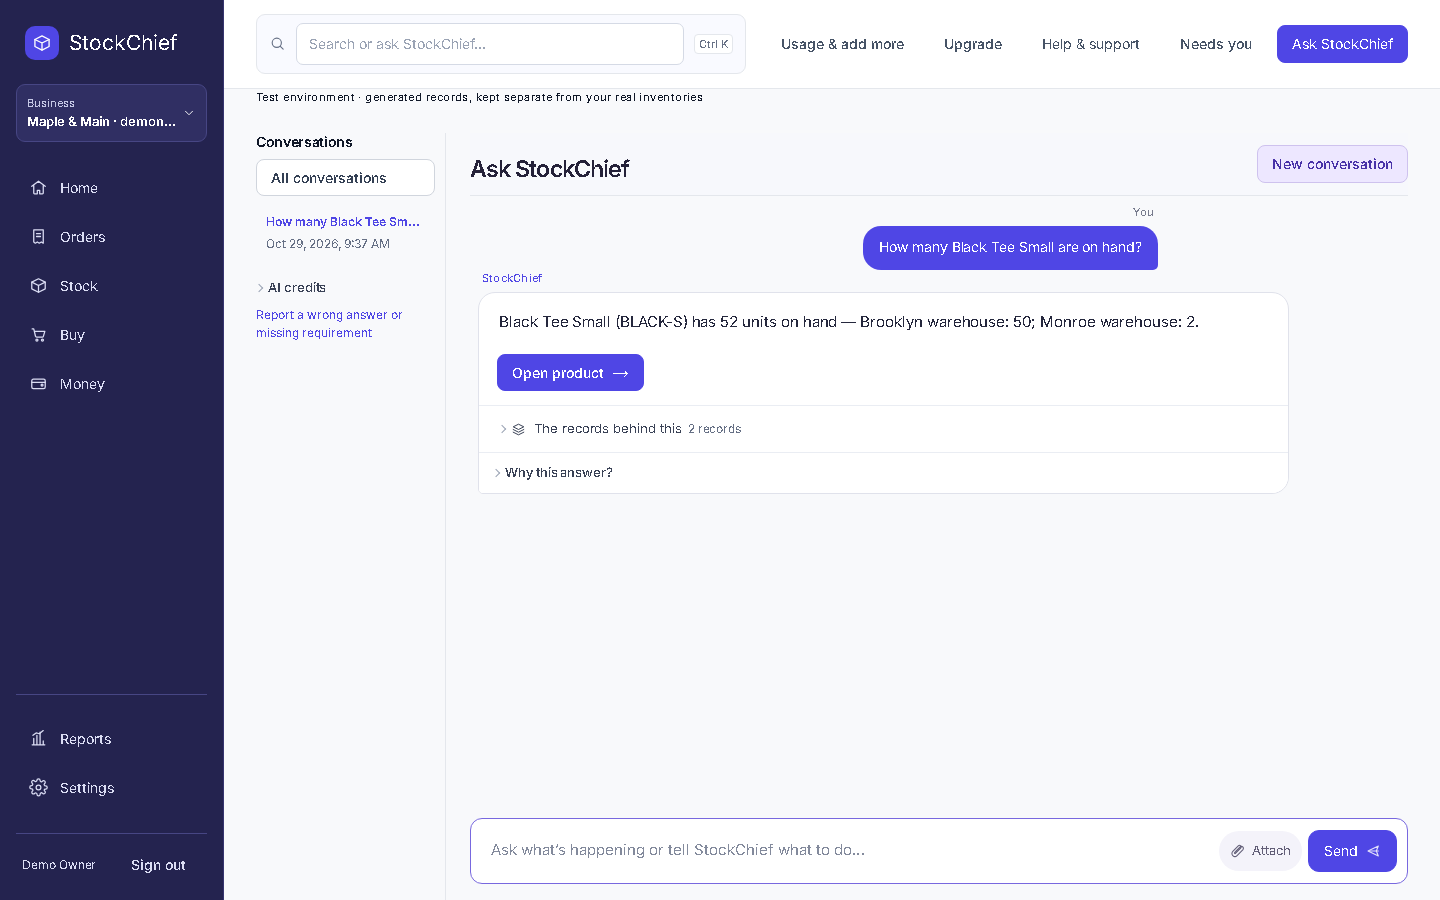
Stock, orders and financial records stay linked to the operations that created them.
Provider credentials are encrypted at rest and excluded from ordinary record and support inspection views.
Membership and permissions scope operational requests to the correct business.
Supported workflows use transaction and idempotency checks. Uncertain provider outcomes can require review before another attempt.
Approve the areas and duration of read-only support inspection, and revoke access when you choose. Inspection is audited.
Merchant payments and postage use the accounts you connect. Provider permissions and supported capabilities still apply.